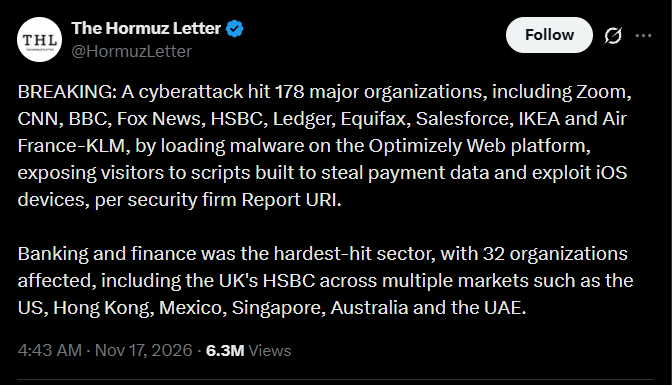
A recent cyberattack has compromised the websites of 178 organizations, exposing visitors to malware designed to redirect cryptocurrency transactions and steal sensitive financial information. Notable affected entities include major corporations like HSBC, the BBC, Salesforce, and the hardware wallet provider Ledger.
The attack took advantage of a vulnerability within Optimizely’s website optimization platform, which allows businesses to experiment with site layouts and content. By exploiting this weakness, attackers injected malicious JavaScript into customer projects, circumventing direct breaches of the affected companies’ servers. Although the harmful code has reportedly been eliminated and the vulnerability addressed, the full scope of the damage remains uncertain.
Vulnerability in Optimizely’s Platform Exposed Websites
The exploitation occurred on November 16, as stated by cybersecurity firm Report URI. The vulnerability in Optimizely’s account registration process allowed the attacker to distribute malicious instructions through the websites of its clients.
Upon visiting an impacted page, visitors could encounter the harmful code without any knowledge of the compromise. The severity of this incident lies in the fact that it affected a large number of organizations simultaneously, including not just retail giants like HSBC and Salesforce but also financial platforms such as Ledger.
Malware Capabilities and Financial Risks
The malware was specifically designed to identify and replace cryptocurrency wallet addresses shown on websites, altering them to redirect funds to attacker-controlled wallets. This manipulation targeted multiple blockchain networks, including Bitcoin, Ethereum, Solana, and others.
Visitors attempting legitimate cryptocurrency transactions could unknowingly paste the altered address into their wallets, leading to unauthorized fund transfers. Additionally, the malicious code was capable of capturing sensitive information such as credit card numbers and cookies, further exacerbating the financial risks.
Researcher Scott Helme noted that of the organizations compromised, six were related to cryptocurrency trading. The attack reportedly led to the acquisition of approximately $7,040 in Bitcoin, a figure that has not been independently verified, while potential financial losses and the extent of data breach remain unknown.
The Ongoing Threat of Third-Party Services
One alarming aspect of this incident is that attackers did not need to breach individual websites directly; they exploited a trusted service utilized by various companies. This tactic allowed the malicious code to propagate through a broad network, impacting many visitors.
Cybersecurity firm Hudson Rock identified similar malicious code in three other web services, suggesting this campaign may have wider implications beyond the Optimizely incident. Address substitution, the primary method used in this attack, is a known strategy for cryptocurrency theft, complicating user transactions without raising immediate suspicion.
Currently, researchers have not established any links between this campaign and artificial intelligence technologies. optimizely has attributed the incident to its flawed signup process, and investigations are ongoing.
This incident raises significant concerns amidst reports of increasing vulnerabilities in software services. Google’s threat intelligence team revealed a doubling of monthly vulnerability disclosures from January to July, highlighting escalating risks for online services.
As shared website infrastructures remain common across various organizations, this incident serves as a critical reminder of the extensive security risks involved. For users engaging in cryptocurrency transactions, it remains essential to scrutinize wallet addresses carefully before completing transfers.
What are your thoughts on whether third-party website providers should implement stricter security measures? Do you believe that address-swapping malware poses a significant threat to everyday crypto transactions?