Concerns Emerge Over Security of Ledger Cryptocurrency Wallets
Allegations are surfacing regarding a potential breach in the supply chain of Ledger, a prominent manufacturer of cryptocurrency hardware wallets. Recent reports suggest that devices sold in various European stores may not only have been physically modified but also contain spyware.
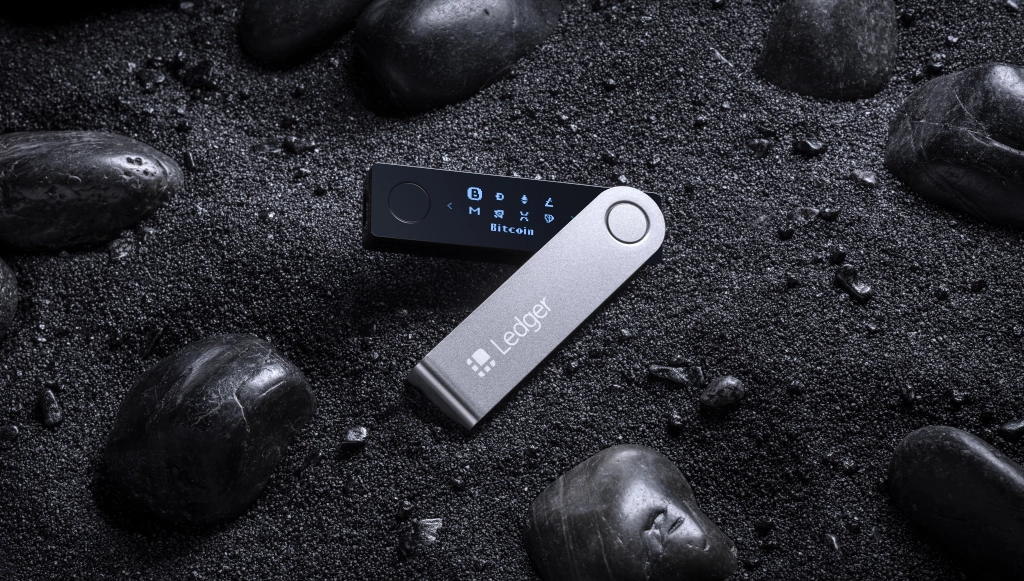
One user, sharing their findings on social media, claimed the integrity of Ledger’s supply chain has been compromised, urging the company to consider a product recall to safeguard its customers. This user reported that they discovered physical alterations on two different Ledger devices obtained from separate retailers in Europe. After purchasing a second device, the user documented the unboxing and found spyware embedded within the device.
Both devices allegedly included unauthorized components, such as cables and an LTE communication module, which are not part of the original design. These additions raise concerns that they may be utilized to extract data from the wallets.
The user suggested that the situation may point to a widespread supply chain attack rather than just an isolated case, particularly since the retailer operates over 1,000 stores across 11 European countries. However, no conclusive evidence has been presented indicating that other Ledger devices from these stores are similarly compromised.
Investigation Focuses on Distribution Channels
Initially, the claimant suspected that the compromised devices had been returned and then re-sold. However, information from a store employee indicated that these devices are categorized as non-returnable and are instead sent back to the manufacturer upon return.
The claimant sent the first of the altered devices to former Mt. Gox CEO Mark Karpelès for evaluation, and plans to forward the second device to Ledger for investigation. Ledger has recommended that consumers who bought their wallets from third-party sellers should conduct thorough inspections before use.
Karpelès has previously stated that some Ledger products contained inconspicuous communication modules that could pass the manufacturer’s authentication checks, raising additional alarm about the devices’ security.
Should these new allegations be substantiated, experts believe this incident could represent a larger hardware supply chain attack impacting not just a few devices but potentially a wide range of sales channels throughout Europe. However, the full scope of this issue, including the number of affected wallets and those responsible, has yet to be independently confirmed.
This article is intended for informational purposes only and does not constitute investment advice.